How Cryptocurrency Works: A Really Simple Explanation for Beginners
What Cryptocurrency Actually Is
I’ve been digging into this topic for a while now, and the first thing to understand is that cryptocurrency is just digital money. No physical coins, no paper bills. It lives entirely online and moves through computer networks called blockchains. The basic idea is pretty straightforward - it’s a digital asset designed to work like money: store value, exchange value, and measure prices. But unlike the dollars in your bank account, no government or central bank controls it. The network runs on code and math, spread across thousands of computers around the world.
Some people call it “crypto asset” instead of currency because there’s still debate about whether it fits the textbook definition of money. Others say it’s digital money because you can buy, sell, transfer, and spend it. Its price comes down to supply and demand, same as anything else. Webster’s Dictionary added the word “cryptocurrency” back in 2018, and one overview puts the number of users worldwide at over 560 million. Yet a 2024 survey found that 90 percent of Americans don’t really grasp the fundamentals. If that’s you, you’re in good company.
How It Differs from Regular Money
Traditional money comes in two forms: physical cash and electronic bank deposits. Cryptocurrencies like Bitcoin are digital-only, decentralized, and verified by a network of computers instead of a central bank. Governments protect regular money against counterfeiting through laws and banking systems. Crypto uses cryptography, distributed ledgers, and consensus mechanisms instead.
Money needs to do three things: let you buy stuff (medium of exchange), hold purchasing power over time (store of value), and serve as a yardstick for prices (unit of account). Crypto can fill all three roles, though how well it works varies a lot between different coins. Bitcoin and many others have a fixed maximum supply - Bitcoin caps at 21 million. That scarcity is baked into the code. Regular money? Central banks can print more or pull it back whenever they want. Some other cryptocurrencies don’t have a hard cap and create new tokens on a schedule.
One practical difference: sending crypto across borders can be cheaper than bank wires or card networks. Historical examples show crypto transaction costs around 0 to 1 percent, versus 2.5 percent or more for credit cards. But those numbers shift with network congestion, which blockchain you use, and what service you’re on. It’s not universally cheaper every time.
Other stated advantages
- Access for anyone with an internet connection and a compatible wallet
- Direct transfers between users without a bank in the middle
- Cross-border payments that don’t hop through multiple banking systems
- Transactions broadcast immediately, no waiting for check clearing
- Digital records shared across many network nodes
- Potentially lower costs for small transfers and international payments
- Programmable rules through smart contracts on supported chains
These benefits do not apply identically to every cryptocurrency. A transaction can cost more during periods of network congestion.
Also worth noting: a central bank digital currency (CBDC) is not the same thing. A CBDC is digital money issued by a country’s central bank, pegged 1-to-1 to the national currency. It’s designed to be stable because it’s backed by the government. Independent crypto assets don’t have that backing.
The Four Core Properties
Cryptocurrency is usually described through four connected properties: decentralization, cryptography, transparency, and immutability. Let me break each one down.
Decentralization means no central bank, government, or admin controls the network. Transaction data lives on participating computers (called nodes) instead of one server. If some nodes go offline, others keep the ledger running.
Cryptography protects everything. It proves a transaction was authorized by the private key holder, that the data hasn’t been tampered with, that the sender hasn’t already spent those funds, and that only the intended recipient can use the output. It also orders blocks and transactions through hashes and network rules. A digital signature shows the private key owner approved the transaction - but broadcasting the signature doesn’t reveal the private key itself.
Transparency means the ledger is public. Anyone can inspect transactions, blocks, and network rules. Addresses don’t automatically show legal names, but every transaction tied to a public address stays visible forever.
Immutability means recorded data is designed to be extremely hard to change. Each transaction has a unique cryptographic hash. Each block contains hashes linking to its transactions and the previous block. Change the data, the hash changes, the chain breaks. To rewrite history, you’d have to redo every affected hash and convince the network to accept your version. That’s practically impossible on major networks - but it’s a design property, not an absolute guarantee. If one entity controls enough mining or staking power, they could reorganize recent blocks.
Immutability is a design property rather than an absolute guarantee.
Scarcity is an extra property for some coins. Bitcoin’s 21 million cap and decreasing issuance schedule create scarcity, which can affect supply and demand. But scarcity alone doesn’t guarantee any particular market value or return.
Cryptocurrency Basics: Definition, Blockchain, and Investment Pros/Cons
How a Blockchain Actually Works
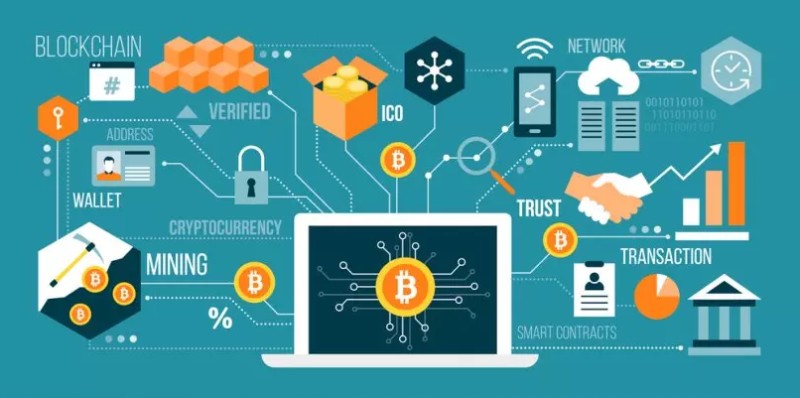
A blockchain is a distributed digital ledger. The name comes from how transaction records are grouped into blocks and linked in a chain. Each block holds transaction data plus a reference (usually a hash) to the block before it.
Here’s the basic flow: transactions are created and broadcast, nodes receive and verify them, valid ones get grouped into a candidate block, miners or validators reach consensus on the block, the completed block links to the previous one, and new blocks stack on top creating confirmations. Because the data is spread across nodes, the network keeps running even if some computers fail. No single server holds the only copy.
Blockchains are append-only. Once data is in a block, changing it would alter the block’s hash and break every link after it. Participants can compare their copies and spot discrepancies. That’s why history is described as practically tamper-resistant. Consensus is how the network agrees on which block belongs in the accepted history. Proof of Work and Proof of Stake are two common mechanisms, but others exist.
A blockchain can record more than currency transfers - it can store records, contracts, ownership references, digital assets, application instructions, and other data. In crypto networks, transactions usually represent fund transfers. In decentralized finance, they can represent token operations, smart contract execution, liquidity activity, and asset exchanges. Each block added after your transaction’s block counts as one confirmation. More confirmations mean less chance of reversal.
Digital Wallets, Addresses, and Private Keys
Owning cryptocurrency doesn’t mean holding a physical object. Ownership is just an entry in a public ledger, controlled through cryptographic keys. You create a wallet on your computer, phone, or a specialized hardware device. The wallet generates or manages key pairs: a private key to sign transactions, a public key to verify signatures, and a public address (derived from the public key) where people send funds.
The public address is safe to share - it doesn’t reveal the private key and can’t be used to spend funds. The private key must stay under your control (or your custodian’s). Wallets also show balances and build transaction messages: they figure out which previous outputs you can spend, select inputs, create change outputs, deduct network fees, and broadcast the signed transaction. Some wallets keep only a partial copy of the blockchain and rely on other nodes; full nodes keep the complete chain.
Wallets come in a few flavors: self-custodied software, hardware wallets, or accounts on centralized exchanges. Self-custody gives you direct control but makes key management your responsibility. Exchange custody is easier for beginners, but you’re trusting the exchange to protect your assets. One security note: the system providing a private key has no built-in recovery if you lose it. Some wallet services offer backup or recovery via seed phrases. If all keys and backups are gone, the crypto stays on the ledger but nobody can access it.
The distinction between a public address and a private key is fundamental. The public address tells the network where funds should be sent. The private key creates the signature proving that the owner authorizes their use.
A merchant can request a Bitcoin address from their wallet. The address comes from hashing the merchant’s public key, which lets the public key be shared safely if needed. The payer gets that address through email, a website, a payment request, or another method.
Simple Guide to How Cryptocurrency Actually Works
What Happens During a Transaction
A transaction starts when you open your wallet, enter the destination address and amount, pick the network and asset, and authorize the transfer. Your wallet creates an electronic message with sender and recipient info, the amount, and a timestamp.
Here’s a simplified lifecycle: your wallet finds previously received funds (outputs) you can spend, builds a transaction using those as inputs, signs it with your private key, broadcasts it to peer-to-peer nodes, nodes check the signature, format, amount, and whether the funds were already spent, valid transactions enter the mempool (waiting area), miners or validators collect them into a candidate block, the network reaches consensus, the block joins the blockchain, and later blocks add confirmations reducing reorganization risk.
A key distinction: transactions broadcast almost instantly, but confirmations take time. As one technical comment put it: “Transactions are instant. Confirmations are not.” Some sources say blockchain transactions can never be reversed. A more detailed view distinguishes pending from confirmed: pending transactions can stay unconfirmed, and transactions in a block that loses a fork can be reorganized. More confirmations make a transaction increasingly secure, though sources differ on whether “never reversed” is absolute or practical.
Transaction fees serve a few purposes: they compensate the miner or validator who includes your transaction, and a higher fee can get you priority when block space is tight. Bitcoin miners also get newly issued bitcoins for validating blocks. On Proof of Stake networks, validators may get new tokens, fees, or both. If someone tries to spend the same output twice, nodes spot the conflict and consensus decides which one ends up in the accepted chain.
Why Digital Currency Needs Signatures and Serial Numbers
A simple digital cash design runs into two big problems: you could copy the same digital message and spend it repeatedly, or someone else could forge a message that looks like it came from you. An early system called Infocoin tackled forgery with signed transfer messages - Alice signs “I’m giving Bob one infocoin” with her private key, and anyone can verify it with her public key. But the same message could be copied, so each unit needed a unique serial number.
A traditional bank could issue serial numbers, track ownership, reject spent units, and update its ledger. That works but relies on a central institution. Bitcoin removes the bank by having participants collectively maintain a public ledger. Everyone keeps a record of which unit belongs to whom and which transactions happened. When Alice transfers to Bob, nodes check the signed message against their ledger copies. After enough participants accept it, everyone updates their local ledger.
But there’s still a double-spending problem: Alice could send the same unit to Bob and Charlie before either transfer is widely recorded. Both see an apparently valid unit. The fix: recipients broadcast the proposed transaction to the network instead of accepting it alone. Other nodes check ownership and flag conflicts. If Alice tries to double-spend, the network catches it. The question becomes: what counts as “enough” participants? The network doesn’t know the total number of users, and one person could create many identities. Proof of Work was introduced to make identity count less by requiring computational work instead.
Proof of Work and Bitcoin Mining
Bitcoin uses Proof of Work (PoW). Miners collect pending transactions, verify them, do computational work, and compete to add the next block. The first miner to solve the puzzle under the current difficulty wins the right to submit the block.
Proof of Work combines two ideas: making it computationally costly to validate and extend the chain, and rewarding miners for doing that work. The cost makes it expensive to create fake identities for fraudulent validation. The reward encourages people to spend computing resources on honest validation.
Bitcoin’s proof-of-work search uses a fixed hash function and repeated variation of a value called a nonce. In a simplified example, you’re looking for a hash with enough leading zeros. More zeros = harder puzzle. A cryptographic hash behaves unpredictably - changing one character completely changes the result. Bitcoin doesn’t directly require leading zeros; it compares the block header hash to a numerical target. The target adjusts so blocks average about ten minutes, though actual intervals vary from a minute or two to twenty minutes or more.
A miner’s chance of solving a block is roughly proportional to their share of total network hash power. One percent of hash rate ≈ one percent chance. A dishonest party would need massive resources to consistently influence validation. When a valid block is found, its transactions are ordered and linked to the previous block. Other nodes verify the proof of work and add the block to their chains.
Sometimes two miners find valid blocks at nearly the same time, creating a temporary fork. Bitcoin’s rule: miners work on the branch with greater cumulative proof of work (often called the “longest chain” rule). If one fork pulls ahead, miners on the shorter branch switch. Transactions from the abandoned branch go back to pending queues.
The 2013 protocol account considered a transaction confirmed when it appeared in the longest chain with at least five more blocks after it - six confirmations total, roughly an hour at ten minutes per block. Many users and merchants accept fewer confirmations or just seeing it in the network. Proof of Work alone doesn’t prove every transaction is valid - nodes must separately check data and reject double-spends or invalid scripts. Reversing a transaction after several confirmations would generally require over 50 percent of total network mining power.
A Curated Collection Explaining How Cryptocurrency Works for Beginners
2025 Beginner's Guide to Cryptocurrency Types and Tips
Bitcoin Mining Rewards and Supply
Mining creates new bitcoins as a reward for validating blocks. The reward is part of Bitcoin’s predetermined monetary supply. It started at 50 BTC per block, halved to 25 BTC at the first halving, and halves every 210,000 blocks (roughly every four years). The design projects the reward dropping below one satoshi around 2140, after which new issuance stops and miners rely solely on transaction fees.
Different sources report different figures because they were written at different times: a late 2023 overview said 6.25 BTC per block, a mid-2024 overview said 3.125 BTC. The differences reflect the halving cycle and publication dates, not conflicting simultaneous rewards. Transaction fees are expected to keep miners motivated after new coin issuance ends. The amount needed will vary with network conditions and mining costs. Bitcoin’s max supply is 21 million. After all are mined, blocks still get validated but no new supply is created through block rewards.
How Forks and Double Spending Are Handled
Two conflicts can occur: a block contains an obviously invalid transaction (like spending the same output twice), or two individually valid transactions compete by spending the same output in separate blocks or chains. Nodes reject obviously invalid blocks. When two valid but conflicting transactions compete, consensus selects the one in the block with the strongest accepted proof of work. The loser gets rejected, placed in another block later, or reorganized away.
The public ledger alone doesn’t prevent double spending. The distributed network, transaction validation, ordered blocks, consensus rules, and accumulated confirmations work together to make conflicting spends unlikely to be accepted. A 51% attack doesn’t automatically let an attacker create valid bitcoins or spend someone else’s coins - transactions and scripts must still follow network rules. But controlling majority hash power could let an attacker reorganize recent blocks and increase the chance a conflicting transaction stays in the chain.
Proof of Stake and Crypto Staking
Proof of Stake (PoS) is an alternative consensus design. Instead of miners competing through computational work, validators lock or “stake” native tokens as collateral. Networks use that stake, plus network-specific selection rules, to choose or probabilistically assign validators who create and verify blocks.
Sunny King and Scott Nadal introduced the concept in 2012 as a response to Bitcoin mining’s energy consumption. King launched Peercoin in 2013, the first crypto to use staking for validation. Ethereum’s Merge in September 2022 switched its consensus from PoW to PoS, making staking core to its operation. At the time of a 2024 overview, Ether’s market cap was reported over $380 billion.
Key differences: PoW miners compete using computing power; PoS validators stake tokens and are selected per network rules. A PoW miner competes with hardware; a PoS validator risks locked tokens. Selection odds often rise with the amount staked. Validators generally create blocks, verify transactions, and earn new crypto plus fees. Delegators lock tokens and assign them to validators, earning a portion of rewards. Because their capital is at risk, validators and delegators are financially incentivized to follow rules.
A validator runs a node and stakes native tokens as collateral. Malicious behavior can trigger “slashing” - part of the stake is removed. Ethereum’s validator minimum was 32 ETH in a 2024 overview. A delegator participates without running a validator, locking crypto and delegating to a validator, earning part of rewards but depending on the validator’s operation and reputation. Network minimums vary: Polkadot’s nominators (delegators) needed 502 DOT in that same overview.
Staking methods
- Solo or self-staking: run your own validator node, stake the required amount directly - more control, more technical knowledge needed
- Delegated staking: assign tokens to a validator - no full validator requirement, but you trust their operation
- Pooled staking: combine contributions of multiple holders - operators make validator and strategy decisions, delegators trust the pool
- Centralized exchange staking: stake through exchange services - easier for beginners, flexible timeframes, customer support, but introduces custody, platform, and strategy risks
- Decentralized apps or smart-contract platforms: a smart contract is blockchain-based software that executes automatically when conditions are met
Staking rewards differ by network, role, method, platform, and date. A 2024 overview reported Ethereum validators around 3.6%, Ethereum annual staking rewards about $1.8 billion, Cardano delegators about 4.6%, Polkadot historical rewards about 14.9%. These are dated figures, not permanent rates - rewards vary with network conditions and participation.
Staking distributes influence among token holders, gives participants a financial incentive to secure the network, and may allow users to participate in governance.
Benefits include passive income potential and encouraging holding rather than immediate selling (though price impact depends on broader markets). Main risks: illiquidity during lockup, token price drops before you can sell, unreliable or dishonest validators, counterparty risk from pools or exchanges, smart contract bugs, network attacks, regulatory uncertainty, technical barriers leading to uninformed decisions, and operational mistakes with keys or contracts. Liquid staking lets you stake while keeping a liquid representation (an LST - liquid staking token) that acts as an on-chain receipt. The staked original stays locked while the receipt can potentially be used in other on-chain activity. This introduces contagion and leverage risks.
A Curated Collection Explaining How Cryptocurrency Works for Beginners
Bitcoin Explained Simply with Web Evolution Context
Major Proof of Stake Networks
As of a spring 2024 ranking, the ten largest PoS tokens by market cap were: Ethereum (ETH), Solana (SOL), Toncoin (TON), Cardano (ADA), Polygon (listed as MATIC), Injective (INJ), Algorand (ALGO), MultiversX (EGLD), Tezos (XTZ), and Mina (MINA). A separate overview identifies Polygon’s native token as POL, formerly MATIC - both labels appear in the source material.
Ethereum is a major platform for smart contracts and decentralized apps. Cardano launched in 2017 emphasizing PoS, with a 2024 overview citing 1,000 transactions per second. Polkadot’s DOT focuses on scalability and interoperability. Staking was presented as a way to scale participation in PoS networks - more participation distributes validation, improves attack resistance, and supports governance. Changes in reward structures, incentives, and voting systems may affect how decentralized and accessible these networks remain.
How Bitcoin Transactions Are Recorded
Bitcoin doesn’t operate as a collection of separately identifiable physical coins. It records a sequence of transactions. Ownership is established by tracing an output forward through later transactions until it’s unspent. The first output a wallet receives comes from a previous transaction. If unspent, it can be referenced as an input in a later transaction. A wallet can combine inputs from several earlier outputs and create one or more new outputs.
Each Bitcoin transaction has a transaction hash. Early explanations treated serial numbers as unique coin identifiers, but Bitcoin uses transaction hashes instead - removing the need for a central authority to issue serial numbers. The chain of references eventually reaches either the Genesis block (no previous input, initial output of 50 BTC) or a coinbase transaction at the start of a block (rewarding the miner). Every block except Genesis begins with a coinbase transaction.
A Technical Look at a Bitcoin Transaction
A nearly raw version-1 Bitcoin transaction with one input and one output contains fields like: hash (identifies the transaction), ver (version), vin_sz (input count), vout_sz (output count), lock_time (controls when final, zero = immediate), size (bytes, not monetary value), prev_out.hash (earlier transaction being spent), n (which output from that transaction), scriptSig (sender’s digital signature and public key), value (amount assigned to output), and scriptPubKey (conditions for spending, including address and Bitcoin Script operations).
The recipient gets 0.319 BTC from the first output of an earlier transaction. Tracing that earlier transaction backward eventually reaches a coinbase or the Genesis block. The input doesn’t state a monetary amount directly - it references an earlier output, and the network gets the amount from that referenced transaction. If the earlier output has more than needed, the excess goes to a change output.
A second example with three inputs and two outputs assigns 0.01068 BTC and 4.0 BTC. For a standard transaction: total input value must be at least total output value; the difference is the fee paid to the miner; Genesis and coinbase transactions are exceptions because they create new supply. If you receive 0.2 BTC but need to send 0.15 BTC, you use the full 0.2 BTC input, create a 0.15 BTC output for the recipient, and a ~0.05 BTC change output to your own address. Wallet software handles this automatically - you just specify amount and destination.
Bitcoin’s Script field makes transactions programmable. A simple payment specifies only the recipient’s key can spend it. More complex scripts support conditional payments and smart contract logic - why Bitcoin is sometimes called programmable money.
A Curated Collection Explaining How Cryptocurrency Works for Beginners
Five-Minute Overview of Cryptocurrency Fundamentals
Proof-of-Work Difficulty and Nonce Details
Miners don’t all hash the exact same block because each candidate block can contain different transactions and a coinbase transaction rewarding a different address. Each miner repeatedly varies a nonce or other block data until the block hash meets the current target. If many miners used the exact same candidate block and searched nonces in the same order, faster hardware would have an advantage. Mining pools divide work among members - operators assign nonce ranges or work shares to reduce repeated searching and distribute rewards.
A proof-of-work result is cheap to check. Others verify the submitted block meets the target and contains valid transactions. The expensive work was the search; checking doesn’t require repeating failed attempts. Security partly depends on hash power distribution. One percent of total hash power = correspondingly small chance of solving a block. Large mining pools can centralize significant network influence, though miners may independently switch networks or strategies if a pool becomes problematic.
Proof of Stake vs Proof of Work
Both PoW and PoS verify blockchain transactions without a bank or payment processor. Their selection methods, participation requirements, energy use, and incentives differ. PoW (used by Bitcoin, Dogecoin, Litecoin): miners compete with processing power, first success produces the next block and earns new coins plus fees, difficulty adjusts to influence block time. PoS (used by Ethereum post-Merge, BNB Chain, Cardano, Avalanche, others): validators stake native tokens, selection depends on stake, randomization, staking duration, validator status, and network-specific rules.
PoS validators process transactions and produce blocks, earning fees, priority fees/tips, and sometimes new tokens. Their stake can be slashed for violating consensus rules. Both use economic incentives for honest participation: PoW relies on competition and expenditure, PoS on locked collateral and protocol penalties.
Major Cryptocurrencies and Networks
Bitcoin (BTC), established 2009, is widely recognized as the first and most established cryptocurrency. Attributed to pseudonymous Satoshi Nakamoto (real identity unknown). Decentralized, uses PoW, supply capped at 21 million. Used for payments, investment, and store of value. A mid-2024 overview reported an all-time high around $73,000 - a historical figure, not a permanent price.
Ethereum (ETH), introduced 2015 by Vitalik Buterin, is a blockchain platform for smart contracts and decentralized apps. Its ecosystem supports decentralized finance, NFTs, and more. Ether is the native token.
Other notable cryptocurrencies
- Litecoin (LTC): created 2011 by Charlie Lee, based on Bitcoin with faster blocks and different hashing, focused on faster payments with lower fees
- Dogecoin (DOGE): started from the Shiba Inu meme, developed a worldwide following, one of the best-known altcoins
- Ripple (XRP): distributed-ledger network for fast, low-cost international payments and institutional use, consensus mechanism doesn’t require traditional mining
- Tether (USDT): stablecoin designed to track the U.S. dollar, algorithm limits volatility
- U.S. Dollar Coin (USDC): also tracks the dollar, used for digital transactions and low-cost cross-border payments
- Chainlink (LINK): decentralized network connecting smart contracts with external real-world data
- Stellar Lumens (XLM): low-cost cross-border transactions
- Cardano (ADA): PoS blockchain launched 2017
- Polkadot (DOT): scalability and interoperability focus
- Polygon: native token identified as POL in one overview, MATIC in another, used for fees, staking, governance
- Namecoin: created 2011, identified as the first altcoin
A early 2026 overview reported over 23,000 cryptocurrencies (citing CoinMarketCap), down from thousands in early 2022, with over 17.6 million bitcoins circulating under the 21-million cap. The general altcoin category includes cryptocurrencies other than Bitcoin. One taxonomy separates tokens from altcoins and divides tokens into security tokens (described as securing an account), value tokens (Bitcoin as example), and utility tokens (designed for specific functions). Tokens represent value or function rather than being money in the same form as the underlying unit. Some have been offered through initial coin offerings, compared to stock offerings.
Acquiring and Trading Cryptocurrency
You can acquire crypto several ways: buy with traditional currency on a centralized exchange, use a crypto ATM after creating or identifying a wallet, buy through a decentralized exchange, receive from another person via peer-to-peer service, accept as payment for goods or services, or earn mining or staking rewards. After buying, you need a compatible wallet or custodial exchange account. Buying on one blockchain doesn’t always make the asset usable on another - each network has its own rules, addresses, tokens, and fee system.
A crypto exchange lets users deposit currency or digital assets, view markets, and place buy/sell orders. The exchange matches orders and records balances. Not every exchange supports purchases with national currency. Traditional online brokers may support crypto alongside stocks and bonds - potentially lower trading costs for some activities but fewer crypto-specific features. Crypto exchanges generally offer wider cryptocurrency ranges, wallet storage options, and interest or staking services, with fees varying by asset and transaction type.
CryptoLiteracy.org recommends reputable platforms because fraud and data theft exist in crypto as they do in banking. It cites Coinme as an example describing enhanced security, compliance, and support. KvaPay describes itself as inclusive for beginners and experienced users, with flexible deposits/withdrawals and services for individuals and businesses. Localcoin’s material focuses on buying crypto with cash, pre-selling online, selling for cash, and selling for INTERAC e-Transfer in Canada - showing access methods depend on location and jurisdiction. Identity requirements also depend on service and jurisdiction. A network may be decentralized while an exchange providing fiat access and wallet custody requires identity verification.
buying crypto onlineA Curated Collection Explaining How Cryptocurrency Works for Beginners
Payments, Merchants, and Cross-Border Use
Cryptocurrency works as a medium of exchange. Its digital form permits internet transfers without physical coins. International payments may need fewer intermediary banking systems than conventional remittance.
A 2017 primer listed advantages for merchants: transactions settle without check delays, no debit-card info needed on the blockchain itself, cross-border accounts don’t need to be domiciled in one country, payment costs can be lower than card fees, payments work across time zones, merchants may accept payment without a conventional card processor. Disadvantages included: many buyers/sellers didn’t understand value changes, money-laundering concerns caused hesitation, most merchants didn’t accept Bitcoin, those that did often partnered with exchanges that immediately converted to traditional currency (indicating limited confidence), price volatility could change fiat value between agreement and settlement, public blockchain records didn’t necessarily provide cash-like privacy.
Microsoft, Overstock.com, Dell, Expedia, Subway, and MLS San Jose Earthquakes were listed as accepting Bitcoin around 2014–2016 - historical examples, not a current list. Cross-border assets also exist in networks designed for that purpose: Stellar Lumens as low-cost option, Ripple for international payments and institutions, USDC and USDT when users want a dollar-tracking asset instead of a freely fluctuating price.
using digital currency for bankingInvestment, Volatility, and Value
Some people buy crypto as an investment hoping market value rises. Others use it primarily for payments or applications. Investment behavior is separate from the protocol’s function as a medium of exchange.
Bitcoin has seen large price changes. A 2017 source said it rose ~45,000 percent over five years and gained 150 percent in 2017, then fell 19 percent in three trading days after an all-time high. Those reflect historical conditions. Volatility comes from changing supply and demand. More mining creates new supply while the protocol caps the final total. Demand shifts with adoption, investment interest, regulation, exchange access, and external events. The 2017 source cited Asian investment interest and Japan allowing Bitcoin for online payments as demand drivers.
One historical source argued Bitcoin shouldn’t be a primary investment vehicle due to little-understood, highly volatile markets. It presented decentralization as a possible future hedge against inflation or fiat depreciation since governments don’t directly control Bitcoin’s supply - described as speculative, not guaranteed. Views differ on whether Bitcoin is inflationary, deflationary, or both. Its supply increases on a predetermined schedule until the cap. It can be described as having controlled decreasing issuance. One comment argued it’s inflationary until ~2140 and may experience deflation when coins are lost. Another argued deflation when the Bitcoin economy grows faster than money supply. Others distinguished money-supply inflation from price inflation/deflation experienced by users.
Scarcity isn’t the only value source. One discussion described Bitcoin as a medium of exchange similar to gold: scarce, hard to counterfeit, not a claim on another asset. Others argued market value arises when participants voluntarily exchange it for goods, services, or other assets. A separate overview states crypto doesn’t have the same inherent value as conventional money and is often bought with fiat currency.
Money is like gas in the car – you need to pay attention or you'll end up on the side of the road – but a well-lived life is not a tour of gas stations!
Tim O’Reilly’s response to Bitcoin speculation included that quote, adding he was more interested in crypto as a way to enable new forms of collective behavior than as a way to get wealthy.
Smart Contracts and Decentralized Applications
A smart contract is blockchain-based software that executes when specified conditions are met. Its code can hold or transfer value according to network rules. Ethereum was designed to support smart contracts and dapps. Its infrastructure contributed to decentralized finance, NFTs, and other projects.
Chainlink connects smart contracts to external data through a decentralized network. Such connections are necessary when an application depends on outside information: price feeds, weather data, transport data, or other real-world events.
Bitcoin transactions also include Bitcoin Script instructions in inputs and outputs. The common output sequence - OP_DUP OP_HASH160, a public-key hash, OP_EQUALVERIFY, OP_CHECKSIG - places conditions on how the output may later be spent. Bitcoin’s scripting system supports more than person-to-person payments. Conditional transactions form the basis of programmable financial instruments and advanced smart contracts. Its capabilities, constraints, and history are separate from application-specific blockchains like Ethereum.
what blockchain enables beyond paymentsNative Tokens and Network Fees
Every blockchain generally uses its own native asset to support operations and pay transaction costs. Bitcoin’s is BTC, Ethereum’s is ETH, BNB Chain’s is BNB, Tron’s is TRX, Polygon’s is MATIC or POL depending on the source. You may need the network’s native token to pay a transaction fee. The network and asset must be identified correctly - sending an asset across an incompatible network can result in loss or unrecoverable funds.
Miners or validators are compensated through transaction fees, block rewards, or both. On some networks, higher fees encourage earlier prioritization. On PoS networks, validators may also receive tips or priority fees. Native tokens serve several functions: pay for network computation or transaction inclusion, compensate validators or miners, represent value within an ecosystem, participate in staking or governance, permit transfers using network-specific smart contracts. A token’s value and function depend on its blockchain, supply rules, demand, governance, and permitted uses. A token can’t provide every feature of a different network just because both are labeled cryptocurrency.
Security, Fraud, and Hacking
Crypto security depends on private-key control, network consensus, software correctness, exchange practices, and the service through which you access assets. Cryptographic systems are designed to prevent unauthorized changes and false signatures, but users can still lose funds by exposing a private key, failing to back up a wallet, installing malware, trusting a fraudulent exchange, or sending funds to the wrong address. A copied private key creates uncertainty about ownership because both the original holder and the copy have the same signing authority.
A discussion participant raised the possibility of implementation flaws allowing invalid bitcoins or spending someone else’s coins. Another reported two major historical Bitcoin flaws that allowed both but were patched before large-scale exploitation. The author agreed vulnerabilities are possible in popular open-source software and noted benevolent researchers help find and fix them.
A lost Bitcoin key is generally treated as loss of access, not a transaction reversal. Lost bitcoins remain part of the recorded supply unless the key pair is recovered or the cryptography is broken. Long-term participants have suggested subdividing the satoshi might eventually be needed if a meaningful portion of supply becomes inaccessible. Stablecoins reduce exposure to crypto price volatility but introduce issuer, reserve, regulatory, freeze, and trust considerations. Their value is tied to the dollar rather than generated solely by mining demand.
Public Ledgers, Privacy, and Anonymity
Bitcoin addresses don’t automatically show legal names. Users can hold multiple addresses, and many wallets create a new address for each incoming payment. This makes addresses pseudonymous rather than directly revealing identity. At the same time, the ledger is public. Anyone can trace fund movement, identify reused addresses, analyze address clusters, and follow transactions through exchanges or merchants. Once an address links to an identity through an exchange account, merchant record, public post, or other info, earlier and later transactions may link to that identity.
The source material has differing descriptions: a 2017 summary claimed Bitcoin could be used anonymously with no real name needed. A 2026 overview asserted users could remain fully anonymous during trades. But the detailed 2013 protocol account called the anonymity claim a myth, describing Bitcoin as “perhaps the most open and transparent financial instrument the world has ever seen,” while acknowledging some users take extensive measures to avoid identification. The protocol account said addresses aren’t immediately associated with legal identities, but public-chain analysis can sometimes identify likely owners, and identification could occur retrospectively long after a transaction.
Comment participants didn’t agree on anonymity limits. Some argued public-ledger analysis, address clustering, exchange records, and reused change addresses make Bitcoin “anonymous but traceable.” Others argued carefully acquiring Bitcoin with cash, avoiding permanent identifying records, using new addresses, and employing mixing services could make individual transactions hard to link. The material presents these as competing descriptions, not a single guarantee. A transaction avoids transmitting a name, debit-card number, or bank account number to the blockchain while still becoming associated with an identity through the exchange or merchant handling the off-chain purchase or sale. KYC procedures make that off-chain link more likely.
Identity Verification and KYC
Crypto networks may not have a central account-opening system, but regulated exchanges and service providers can require identity verification. Know Your Customer (KYC) procedures establish that an account holder is a real person, detect fraud, and comply with anti-money-laundering requirements.
Identity methods
- Government-issued document verification
- Selfie or biometric verification
- Face authentication
- Database checks
- Address verification
- Phone verification
- Bank-account verification
- Ultimate beneficial owner checks for businesses
- Screening against sanctions, politically exposed persons, watchlists, adverse media, and address risks
The Travel Rule is a regulatory framework requiring virtual asset service providers to collect and verify information for qualifying crypto transactions. It requires originator/sender info when a transaction exceeds a specified threshold (exact threshold varies by applicable rules). The purpose: reduce crypto use for fraud and money laundering. Identity verification is an additional platform requirement, not a replacement for blockchain consensus. It creates a connection between real-world identity, platform account, and public blockchain addresses. Centralized exchanges may also maintain internal records for trades that never appear as blockchain transactions - only transfers between a platform and an external address appear on the public network.
Decentralization and Concentrated Infrastructure
The base Bitcoin protocol has no central administrator, but practical participation can concentrate at certain points: mining hardware from limited suppliers, a few mining pools holding significant hash rate, exchanges custodying large user funds, wallet providers becoming failure points, merchants controlling the fiat-crypto relationship, large network participants influencing fees, transaction visibility, and consensus decisions.
The protocol account and discussion treated mining-pool concentration, bandwidth limits, denial-of-service attacks, scalability, and wallet infrastructure as unresolved engineering and economic concerns. A full node stores complete transaction history. In a 2013 comment, the blockchain was ~12 GB; another user saw it grow from ~2 GB to ~25 GB in about a year - dated, anecdotal figures. Lightweight or pruning wallets reduce local storage; some services keep centralized chain copies. Suggested scalability approaches include lightweight wallets, pruning historical data, dedicated servers, service providers, larger blocks, and off-chain protocols. Each can alter decentralization. Specialized infrastructure may enable high volume but can concentrate storage, validation, or broadcasting among fewer operators.
Are Transactions Reversible or Irreversible
The sources express finality differently: one overview says blockchain transactions can never be reversed. A detailed protocol explanation shows transactions can remain pending, compete, or enter a chain that loses a fork. Another says each additional block makes a transaction more secure and less likely to be reversed. The 2013 account uses a six-confirmation model to reduce risk of accepting a transaction that later appears in a competing chain.
These refer to different stages. A transaction broadcasts almost immediately, remains unconfirmed, gets included in a block, and gains confirmations. Finality strengthens after confirmations, while “never reversed” is an absolute description that doesn’t account for chain reorganizations or consensus failure.
Anonymity, Regulation, and the “No Regulation” Claim
A historical Bitcoin description said it wasn’t tied to a country or subject to regulation, with easy inexpensive international payments. More recent crypto platforms operate under identity verification, licensing, AML, sanctions, and Travel Rule obligations. Regulation differs by country and activity: a permissionless blockchain transfers assets between participants; an exchange selling to the public may be a regulated financial service; a merchant accepting crypto may have tax, accounting, and record-keeping obligations; a stablecoin issuer may face reserve and redemption rules; a staking provider may be classified by whether it provides custody, validation, or investment services; cross-border services may need to comply with both origin and destination requirements.
KvaPay states it’s operated by Ilavo Group, a.s., holding a license under the EU’s MiCA Regulation supervised by the Czech National Bank. A licensed platform doesn’t make the underlying permissionless network centralized.
Confirmation Times and Payment Finality
Every block after a transaction’s block counts as one confirmation. One confirmation = included in the chain. Six confirmations = five additional blocks in the older model. More confirmations reduce the risk of another branch replacing the transaction’s block. A merchant can accept a low-value transaction immediately after broadcast or wait for more confirmations. Larger values may need more confirmations because reversal would create greater losses.
Expected block time changes with difficulty and network conditions. Ten minutes was the long-term average in the protocol account, not a guarantee. Confirmation time depends on mining activity, fee priority, difficulty, and consensus history. The mempool is the waiting area for broadcast but unconfirmed transactions. Wallets and exchanges calculate different estimates based on fee rates and conditions. A missing or delayed transaction can result from propagation problems, low fees, conflict with another transaction, insufficient inputs, wallet problems, or confirmation in a block that didn’t become the accepted chain.
Problems with Two-Phase Commit
A proposed alternative to Bitcoin’s consensus involved two-phase commit: recipients broadcast transactions and wait ~ten minutes. If no signed evidence of a double spend appeared, they’d accept it. The material identifies unresolved problems: must be hardened against denial-of-service attacks; a malicious participant could create many identities and flood with false reports; a claimed double spend should require a digitally signed conflicting transaction, not an unsupported assertion; must avoid preventing legitimate low-value payments depending on zero-confirmation acceptance; Bitcoin’s PoW already creates an expected time/probability structure for confirmation but doesn’t make every transaction instantly irreversible.
Limits of Proof of Work
PoW raises the cost of manipulating consensus but has limitations: expensive hardware makes mining hard for individuals and encourages pools; validation time varies around target average; a majority hash-rate attacker may delay or reorganize transactions without spending invalid coins; a miner with large power has greater block probability, so accepted history remains governed by economic incentives as well as cryptographic rules; the difficulty target is maintained by network rules, so an interruption or internal fork can divide nodes; miners may intentionally leave out transactions if more profitable, subject to competition; low fees may become less sustainable if block space is limited; as block rewards approach zero, miners depend more on fees; the fee quantity and cost to keep mining secure remain uncertain.
PoW was presented as energy intensive, while PoS was introduced as a possible response to Bitcoin mining’s energy consumption. No exact energy-use statistics were supplied.
Open Questions About Bitcoin Mining and Security
The protocol discussion raised several unresolved questions: how large must the mining reward be for sufficient participation? How will mining distribute across operators or concentrate in a few? What fee level maintains security after block issuance caps? How can small transactions stay economical if fees become important? How should blocks be sized if demand exceeds capacity? How should full-ledger growth be managed? How do nodes handle denial-of-service and bandwidth attacks? How do software vulnerabilities get discovered and patched quickly? How does the protocol behave if underlying cryptography or random-number generation weakens? Could quantum computing affect hashing or signature security? How should transaction malleability be reduced without changing validity rules? How should forks be handled when miners use different software versions? What predictable nonce patterns should mining software avoid? How should zero-confirmation payments balance against double-spend risk? How does a restored wallet sync with a newer blockchain? What happens if a user loses both private key and every backup? How do legal and taxation frameworks interact with pseudonymous public ledgers? How should over 50% mining power be treated differently from under 50%?
The detailed protocol account explicitly cautioned that its double-spending discussion was informal, not a rigorous security proof, and that Bitcoin security continued to be studied.
Bitcoin’s Core Technical Properties
Bitcoin combines several ideas into a system that works without a central issuer or recurring serial-number database: digital signatures prove authorization; transaction outputs form the basic ledger units; inputs reference earlier outputs; outputs assign value and spending conditions; transaction hashes identify transactions; block headers commit to transaction data and the previous block; Proof of Work orders and secures blocks; the longest accepted valid chain serves as primary consensus history; confirmations reduce reorganization chance; halving rules determine new coin issuance; transaction fees remain as miner incentives after issuance ends; public block and transaction visibility supports transparency; Script instructions make some transactions conditional and programmable; the Genesis block and coinbase transactions originate new supply.
If you’re just getting started with learning the ropes , the main thing to remember is that this isn’t magic - it’s a set of rules encoded in software, running on a network of computers, secured by math and economics. The core concepts aren’t actually that complicated once you strip away the jargon. And if you’re wondering how the pieces fit together , think of it as a shared spreadsheet that no single person controls, where everyone agrees on the rules for adding new rows.
There’s a lot more to explore - different coins with different goals, newer networks experimenting with other designs - but the foundation stays the same: digital signatures, shared ledgers, consensus without a central referee, and incentives that make honesty the winning strategy. That’s the part that still feels remarkable to me after all this time.
Comments on “How Cryptocurrency Works: A Really Simple Explanation for Beginners”
No comments yet. Be the first to share your thoughts.